Table of contents
15
By Salman Khan, OSCP+, Founder of XHack, SRT (Synack Red Team member)
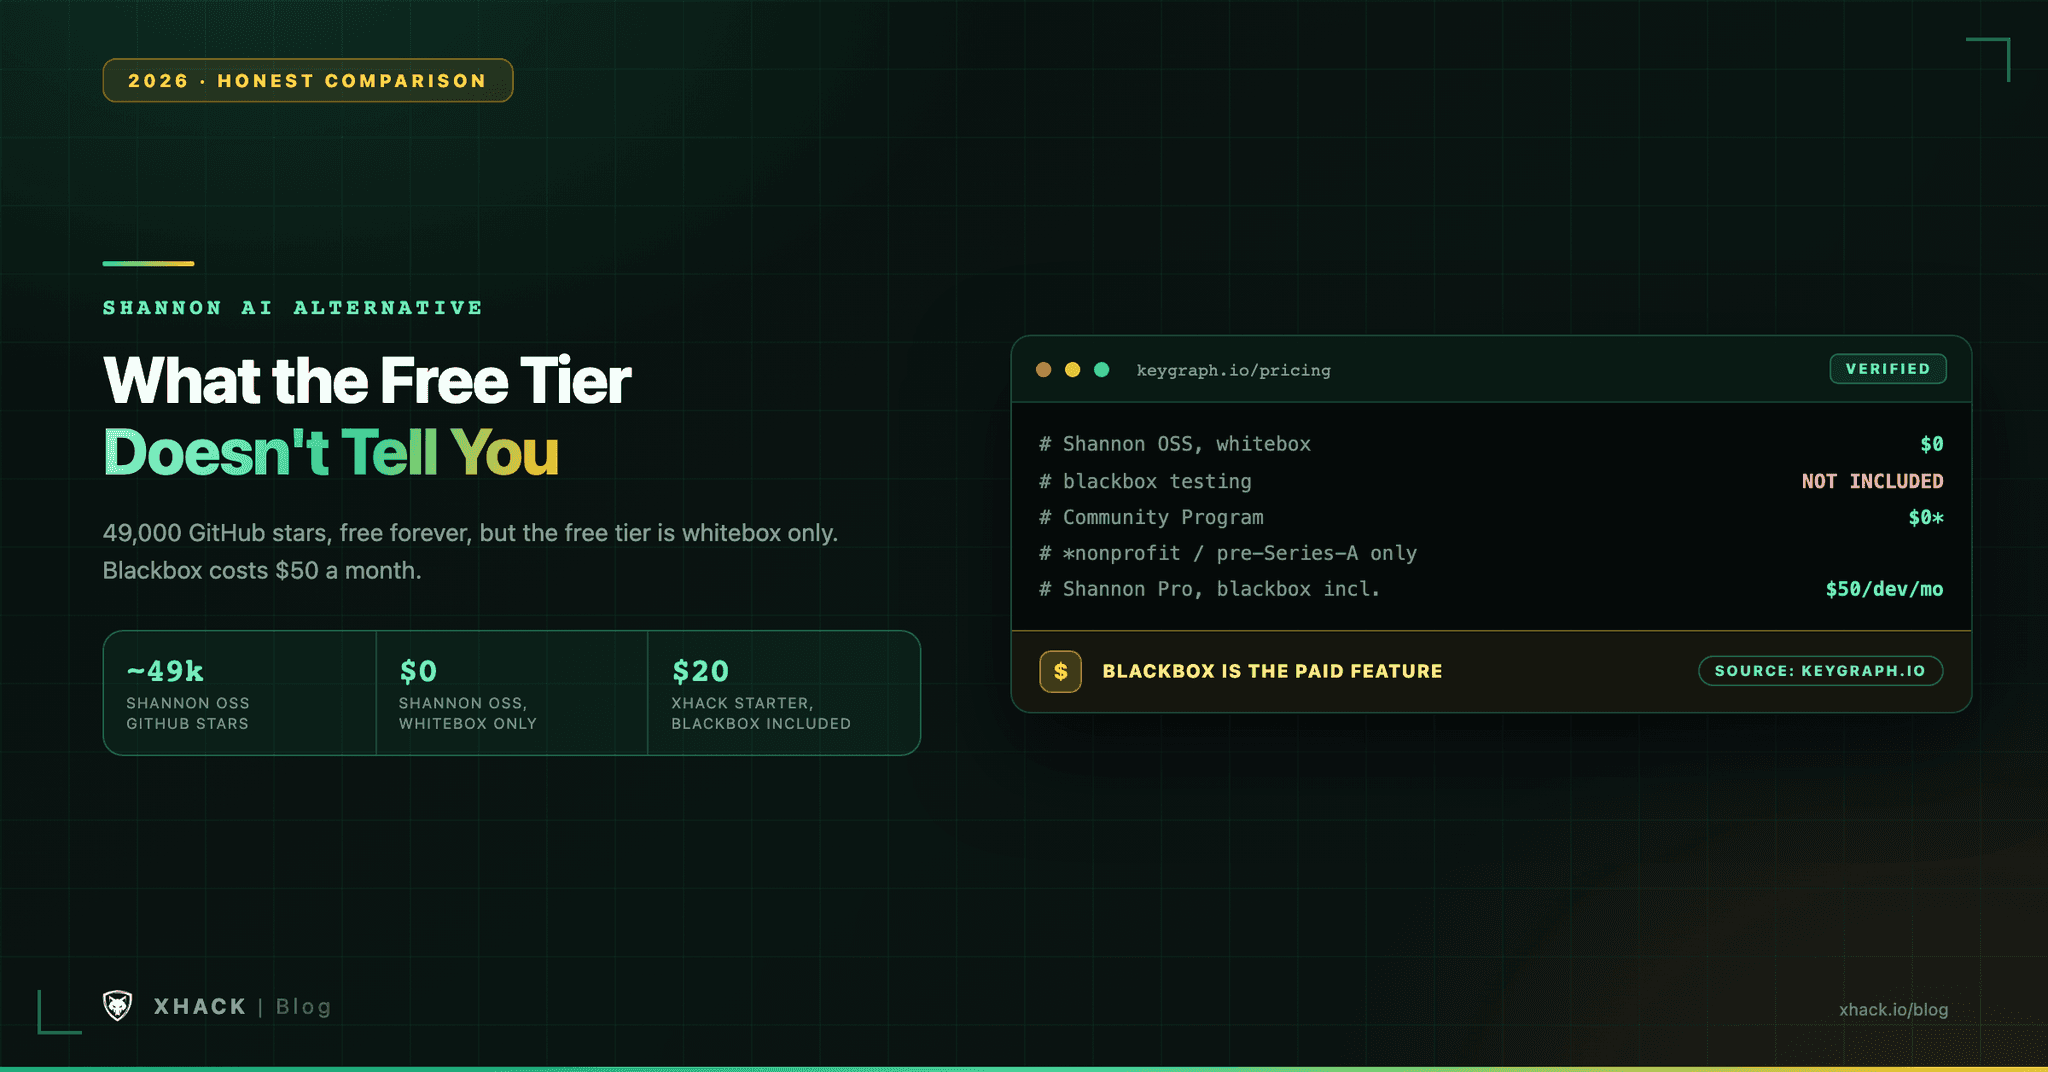
Read this in 30 seconds: Shannon is a genuinely impressive open-source AI pentester, nearly 49,000 GitHub stars, AGPL-3.0, free forever, but its free tier is whitebox only, and that matters a lot if your actual job is hunting bugs in someone else’s live application.
- Shannon’s $0 tier needs your source code. Keygraph’s own GitHub page says the open-source edition “analyzes your source code to identify potential attack vectors” and its quick start tells you to “run a pentest against a source-available target.” Most bug bounty scope is the opposite: a live target you don’t own the repo for.
- Blackbox testing costs money with Shannon. “Tests the running application from the outside, with no source code needed” is listed as a Pro, Enterprise, or restricted Community Program feature on Keygraph’s own pricing page, not the free one.
- The free “Community Program” has a narrow door. It’s $0 while you qualify, but eligibility is limited to U.S. 501(c)(3) nonprofits and pre-Series-A startups, capped at 20 active developers, not solo bug bounty hunters.
- Shannon Pro starts at $50 a developer a month, 2.5x XHack’s $20 Starter tier, for the cloud-hosted platform with blackbox testing included.
- XHack’s $20 Starter does blackbox from day one. Auto Browsing, a built-in browser engine and recon tooling work against a live target with no source access required, which is the default bug bounty situation.
Shannon earned its nearly 49,000 GitHub stars honestly, but the feature a bug bounty hunter actually needs, testing a live target with no source access, sits behind a paywall most solo hunters won’t clear.
Shannon, built by Keygraph, is one of the most visible open-source AI pentesting projects of 2026, and the most-searched Shannon AI alternative question is really a question about what its free tier doesn’t do. It is also a legitimately different product than most people searching “Shannon AI alternative for bug hunters” probably expect. This article covers what Shannon actually does and costs, where its free tier stops short of a typical bug bounty workflow, and where XHack fits as a genuine alternative for the blackbox, external-target work bounty hunting is built on.
Keygraph’s own GitHub page describes Shannon as a source-informed AI pentester: it “analyzes your source code to identify potential attack vectors,” then checks those findings against the running application. It runs five domain specialists in parallel (injection, XSS, auth, SSRF, authorization) plus a sixth exploit agent for other vulnerability classes, and it tries to produce a working exploit for each finding it reports.
It outputs SARIF 2.1.0 by default in exploit mode, which plugs directly into GitHub code scanning or GitLab’s vulnerability report, a strong signal of who it is actually built for: development teams running security checks inside their own CI pipeline, not external researchers probing a target they don’t control.
The honest facts, straight from Keygraph’s own pages:
None of this makes Shannon a bad product, or this Shannon AI alternative comparison a hit piece. It makes Shannon a different product than its free-tier popularity might suggest to someone shopping specifically for bug bounty work.
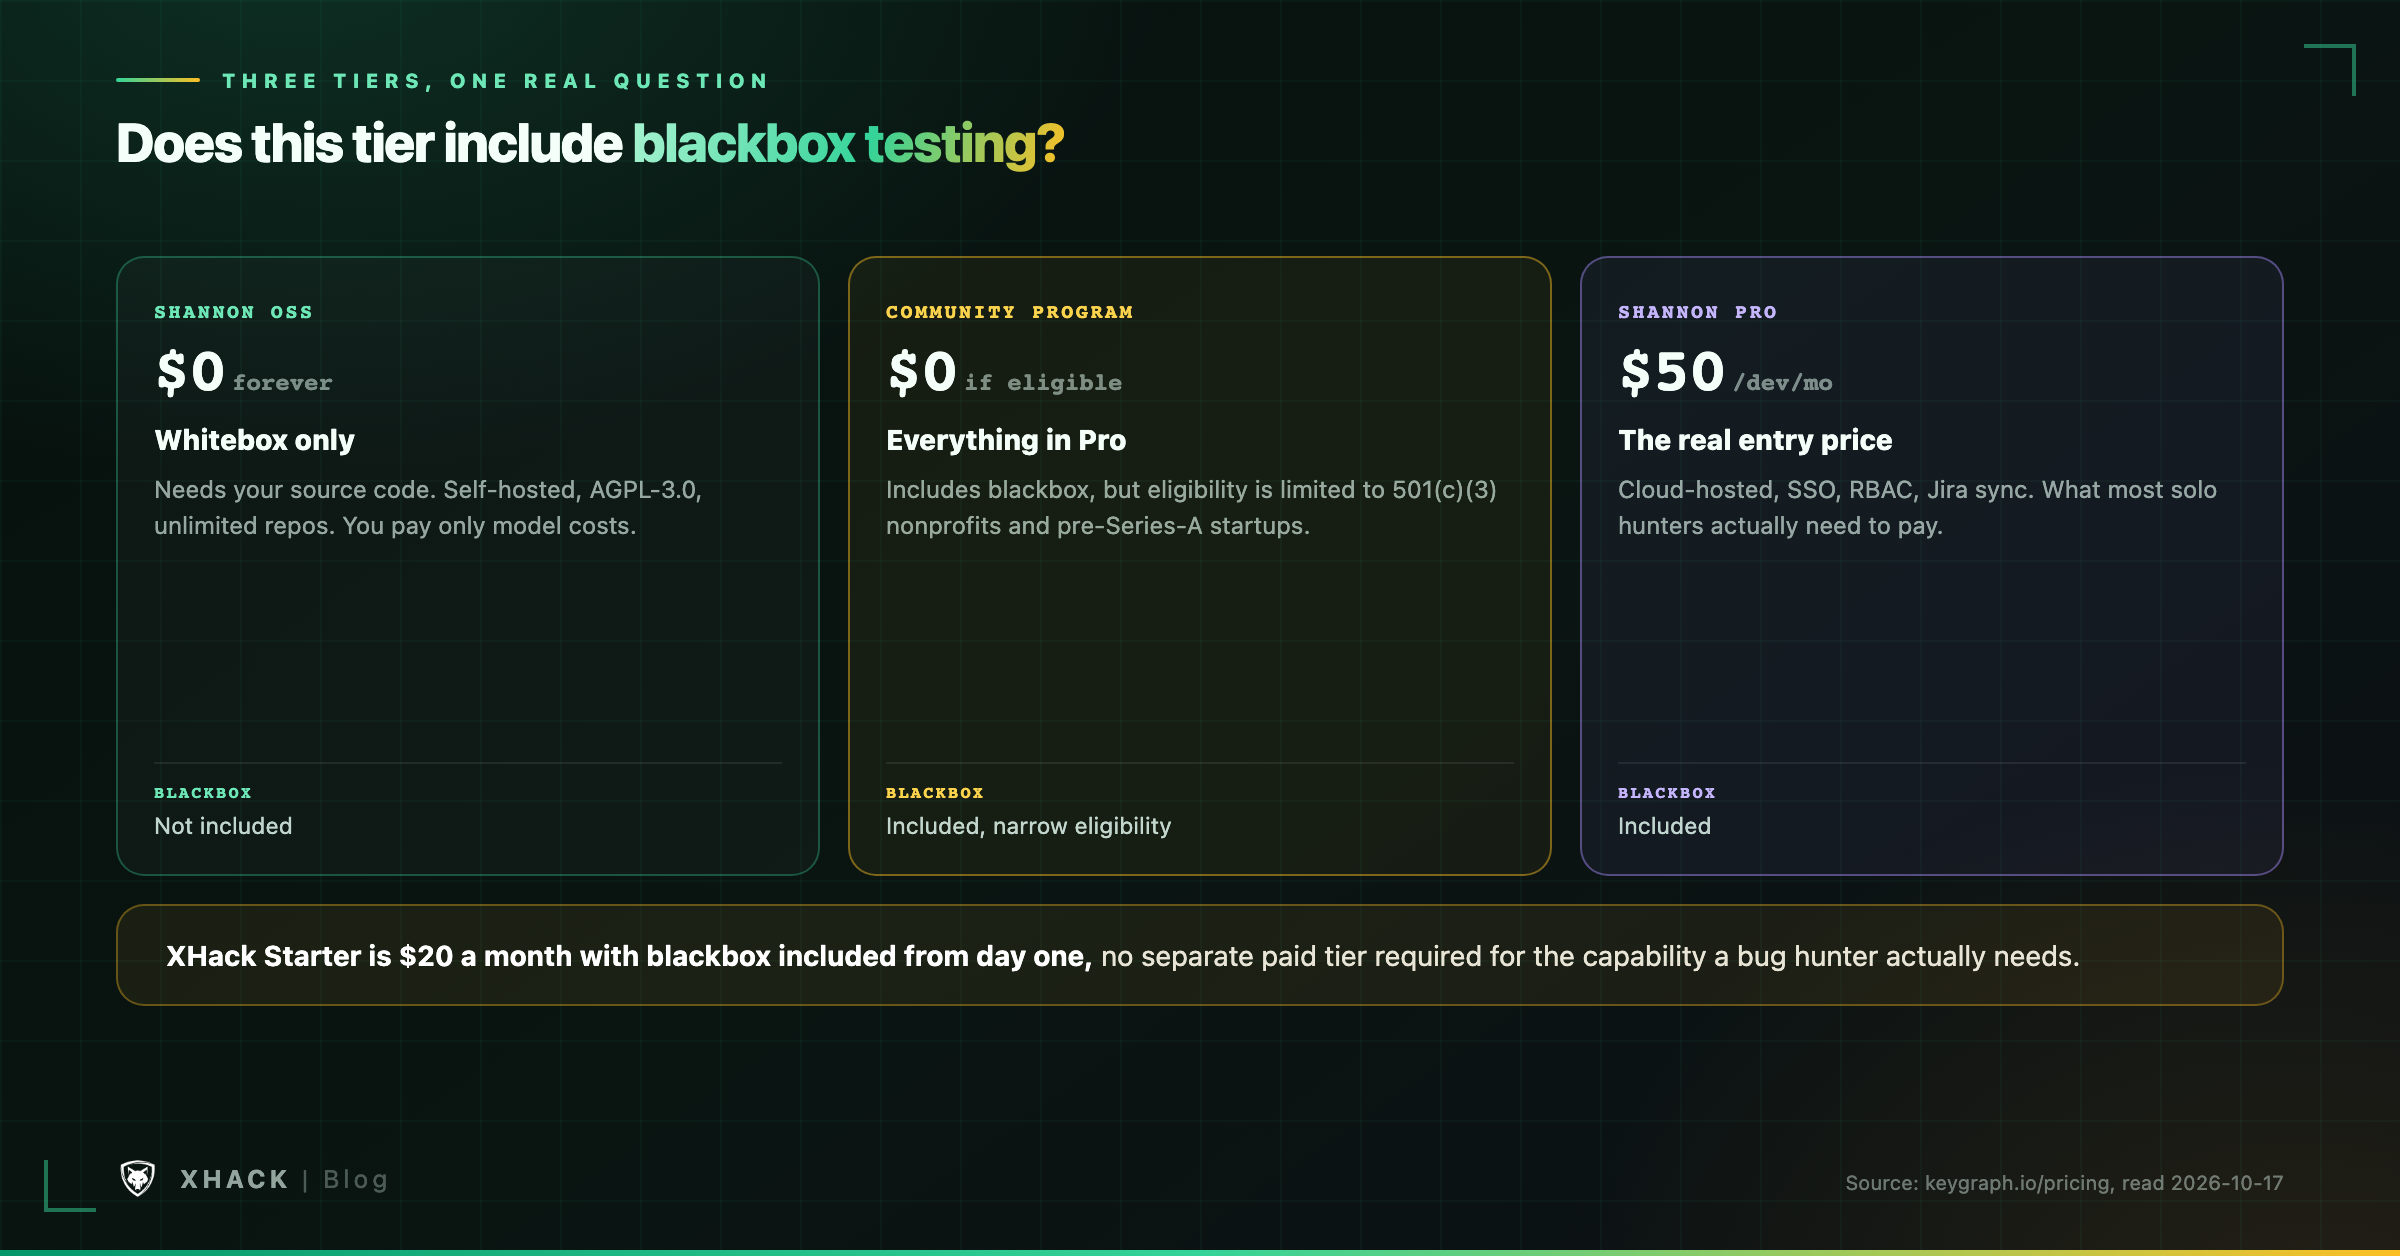
Most bug bounty scope is someone else’s live, running application. You almost never have the source code, and reading it would usually violate the program’s rules even if you did. That is the entire premise of blackbox testing: you interact with what’s exposed, the same way any other attacker would.
Shannon’s free, $0-forever tier is built around the opposite assumption, that you have the source and want to test your own repository, in your own CI pipeline, before you ship. That is a real and valuable job. It is also not the job a solo bug bounty hunter has most of the time.
This is not a strawman. Keygraph’s own marketing is honest about the split: Shannon OSS is whitebox, the Community Program and Pro add blackbox, and a separate product exists specifically for blackbox-without-source use cases. The gap we’re describing is the one Keygraph itself drew.
| Tier | Price | What you get | Blackbox included? |
|---|---|---|---|
| Shannon OSS | $0 forever | Self-hosted, unlimited repos and scans, you pay only model costs | No, whitebox only |
| Community Program | $0 while you qualify | Everything in Pro, every module | Yes, but eligibility is limited to 501(c)(3) nonprofits and pre-Series-A startups, capped at 20 active developers |
| Pro | $50 per developer per month | Cloud-hosted platform, SSO, RBAC, audit logs, Jira sync, unlimited repos and scans | Yes |
| Enterprise | Custom, sales-negotiated | Everything in Pro, self-hosted or air-gapped, dedicated engineer, custom SLA | Yes |
A seat on the Shannon AI alternative’s Pro tier is billed per “active developer,” defined by Keygraph as someone who contributed to a monitored private repository in the trailing 90 days and still has access. For a solo bug bounty hunter, that is one seat, so $50 a month is the real entry price for the blackbox capability most hunters actually want from a tool like this.
As a Shannon AI alternative, XHack’s individual plans start at $20 a month for Starter, with a 7-day free trial, one trial per customer, that ends automatically. Professional is $49 and Elite is $150, both adding BYOK so you can route the agent through your own model provider account.
The difference that matters most against Shannon specifically: XHack’s blackbox capability is not a paid add-on bolted onto a different product line. Auto Browsing drives a real browser against a live target, filling forms, extracting data, taking screenshots and running JavaScript, with no source code input at any point. The platform’s built-in browser engine runs as a docked, multi-tab pane with isolated sessions and full traffic capture, the exact workflow a bug bounty hunter uses against a program’s live scope.
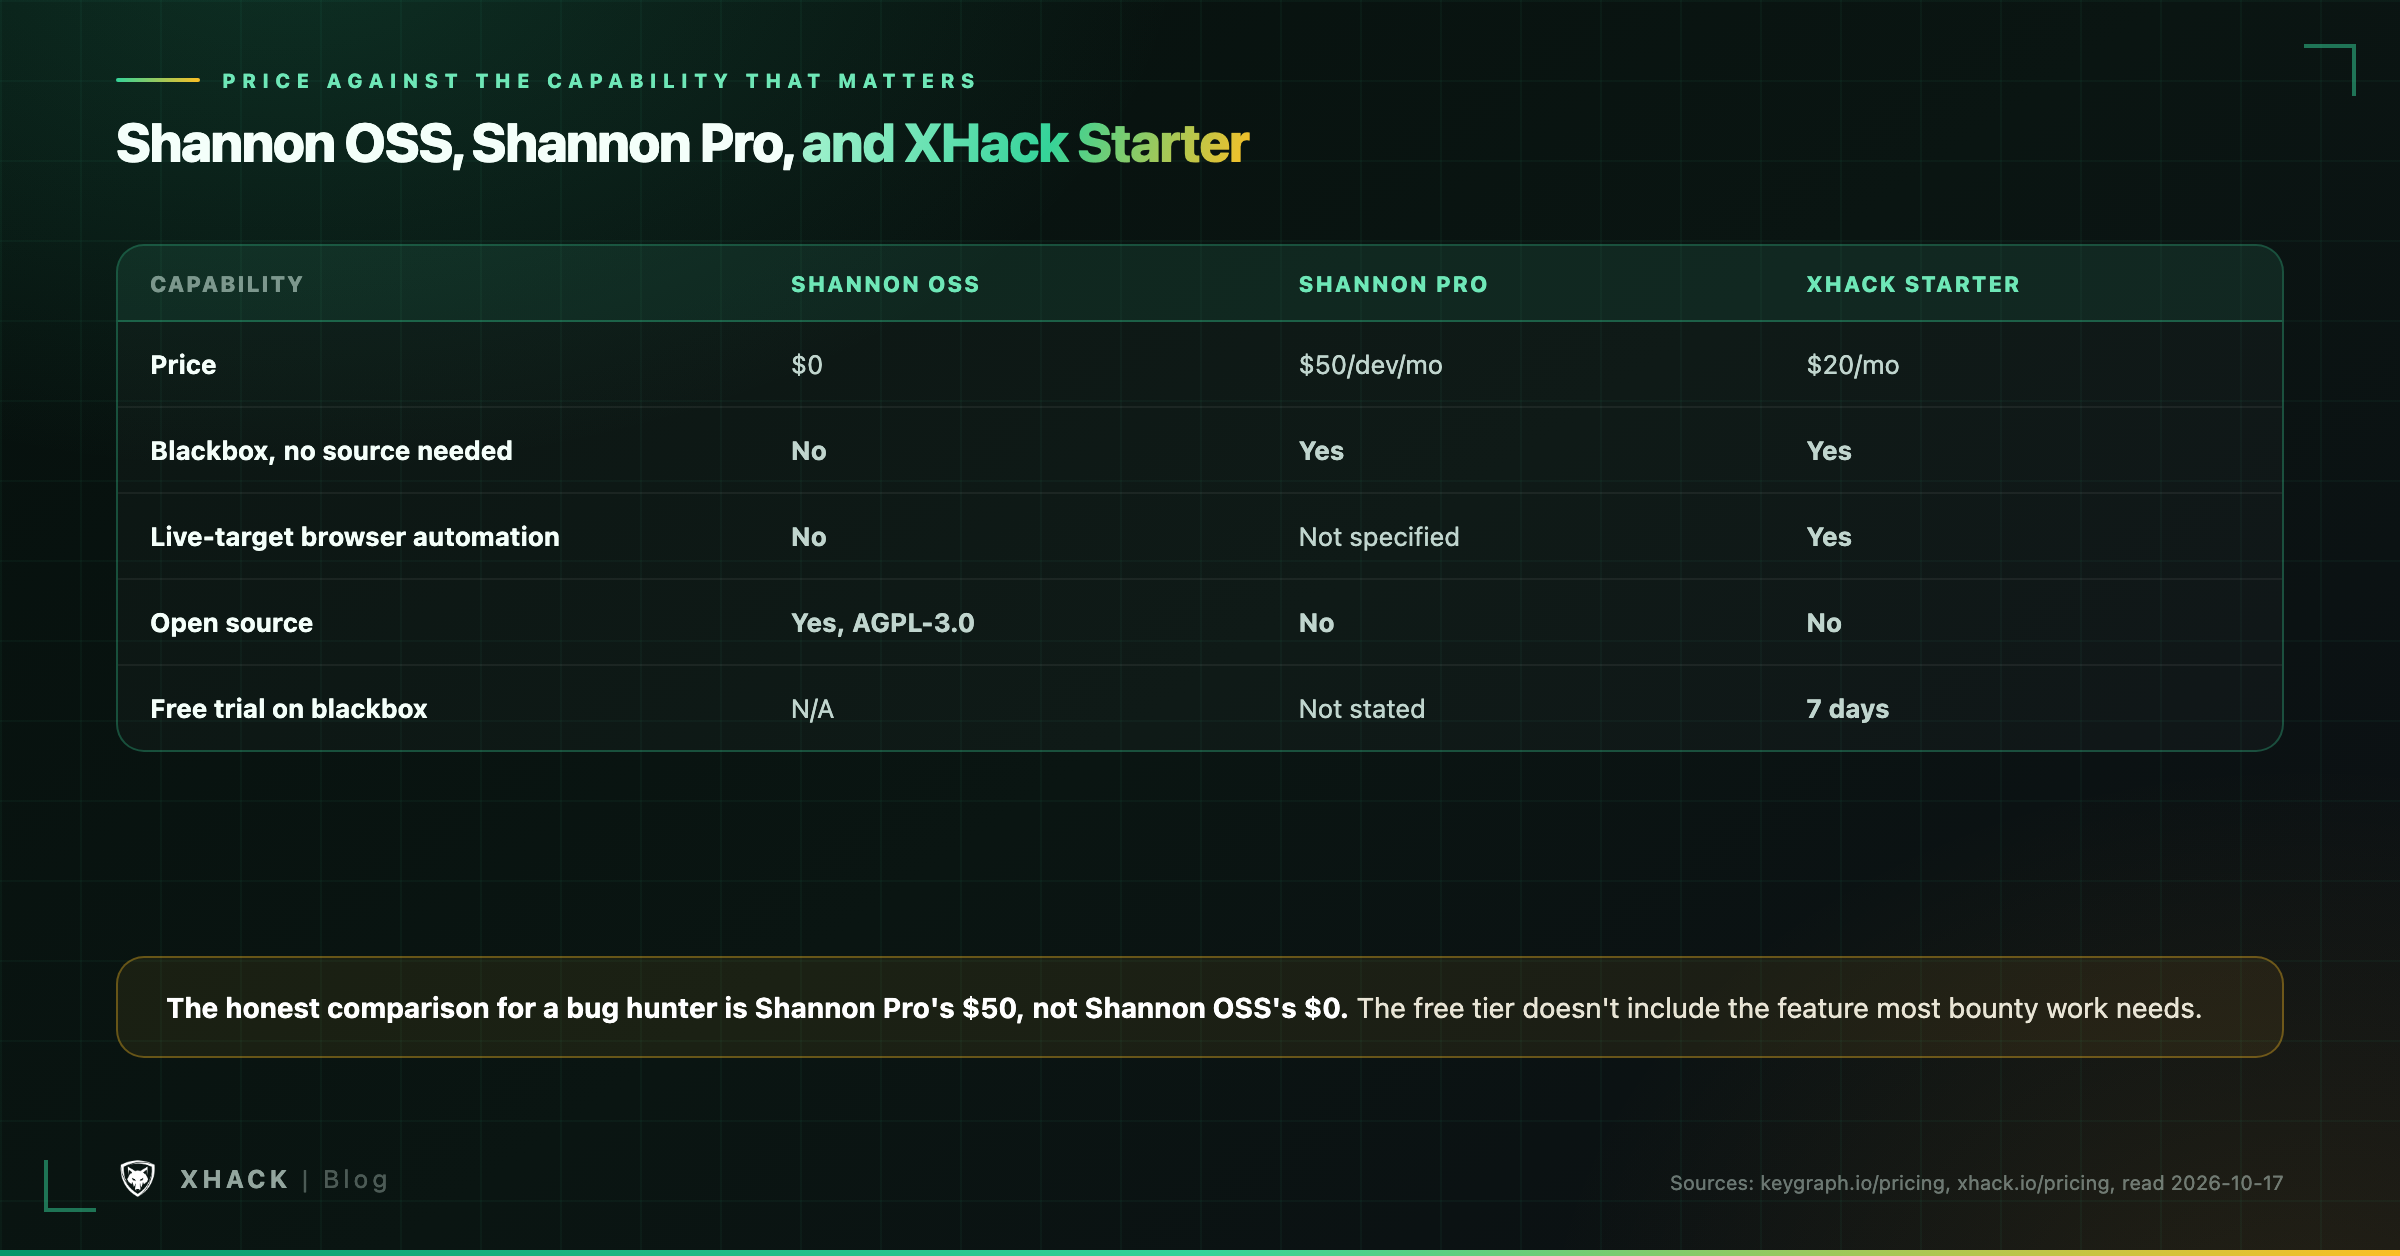
| Shannon OSS | Shannon Pro | XHack Starter | |
|---|---|---|---|
| Price | $0 | $50/developer/month | $20/month |
| Blackbox (no source needed) | No | Yes | Yes |
| Live-target browser automation | No | Not specified on Keygraph’s pages | Yes, Auto Browsing |
| Open source | Yes, AGPL-3.0 | No | No |
| Free trial on the paid capability you need | N/A, the feature isn’t in the free tier | Not stated as free | 7 days |
| Self-hosted option | Yes (OSS) | Enterprise only | No, hosted service |
Where Shannon genuinely wins: if you are a developer or an AppSec engineer who wants free, unlimited, self-hosted whitebox testing of your own repositories inside CI, Shannon OSS is a strong, well-regarded, zero-cost choice, and its SARIF output is a real integration advantage XHack does not specifically target. Nothing in this article disputes that.
Where it falls short for bug hunting specifically: the free tier cannot test a target you don’t have source access to, which describes nearly every bug bounty program’s scope. To get that capability from Shannon, you are comparing against Pro’s $50 a month, not its advertised $0.
Neither side of this Shannon AI alternative question is a universal winner. They are built around different starting assumptions about what you have access to when you start testing.
So yeah, here’s where we talk about our own angle, clearly marked as that, since we build XHack.
XHack combines autonomous recon, exploit development and report generation into one agent-driven workflow, with up to 12 specialized sub-agents by default working a target in parallel. For a bug bounty workflow specifically, that means reconnaissance, Auto Browsing against the live application, JS Hunter reading loaded scripts for exposed secrets, and the HTTP Repeater for manual follow-up, all in one place, without needing a separate product for the blackbox half of the job.
Findings carry severity, location, proof, reproduction steps, the exact request, and a recommended fix, exportable as JSON, Markdown, HTML or branded PDF. Pricing is public on our pricing page: $20, $49 or $150 a month, a 7-day trial on each, Professional and Elite adding BYOK.
The honest part. XHack’s output can be wrong. Our terms say AI output may be incomplete, inaccurate or miss real vulnerabilities, and a hunter is still responsible for validating every finding before submission, exactly the same validation burden Shannon’s own users carry. We are not claiming XHack replaces reading code; if your workflow genuinely needs whitebox, source-informed testing, Shannon OSS’s free tier is a real option we are not trying to talk you out of.
Privacy. XHack does not store your data by design; session data stays on your own machine, deletable any time.
If the Shannon AI alternative’s free OSS tier already covers what you need because you’re testing your own repository, use it, it costs nothing and it’s good at that job. If you need blackbox testing of a live bug bounty target and don’t want to pay $50 a month to get it, start the trial or book a free consultation first, even if the honest answer turns out to be that your current setup already has you covered.
The open-source edition is free forever, AGPL-3.0, and you only pay your own model API costs. But that free tier is whitebox only, meaning it needs your source code. Blackbox testing of a live application with no source access is a Pro, Enterprise, or restricted Community Program feature, not part of the free tier.
Not on the free tier. Keygraph’s own pages describe the open-source edition as source-informed, and point users who want to test a running application without source code toward its paid Pro tier or a separate “Blackbox Pentester” product.
$50 per active developer per month, billed on developers who contributed to a monitored private repository in the trailing 90 days. For a solo bug bounty hunter, that’s effectively $50 a month for one seat, 2.5 times XHack’s $20 Starter tier.
For blackbox testing of live, external targets, yes, that capability is included at the $20 Starter tier rather than gated behind a $50 paid tier of a different product line. For whitebox testing of your own source code in CI, Shannon OSS is a strong, free, purpose-built option XHack isn’t specifically trying to replace.
No. XHack offers a 7-day free trial, one per customer, rather than an unlimited free open-source tier. Shannon’s free tier is genuinely free forever for whitebox use; XHack’s trial is time-limited but gives full platform access, including the blackbox capability Shannon’s free tier doesn’t.
Shannon’s core engine is open source under AGPL-3.0. XHack is a closed-source commercial platform. If running your own self-hosted, auditable, source-available tool matters more to you than blackbox capability out of the box, that’s a real reason to pick Shannon over XHack.
Shannon is a legitimately strong open-source project, and its nearly 49,000 stars are earned. For a bug bounty hunter specifically, the thing to understand before you invest setup time is that the free tier is whitebox, and the blackbox capability most bounty work actually needs lives behind Shannon Pro’s $50 a month or a narrow nonprofit and startup eligibility window.
If your target is someone else’s live application and you don’t have its source code, which describes most bug bounty scope, XHack’s $20 Starter tier includes that capability from the start. If you’re testing your own repository’s source in CI, Shannon OSS is free and genuinely good at that specific job. Pick based on what you actually have access to when you start, not on which tool has the bigger star count.
Categories
Related articles