
About XHack
Certified Cybersecurity Experts
XHack is a cybersecurity firm with OSCP-certified experts providing VAPT, Red Teaming, SOC Services, Threat Intelligence, and GDPR Compliance. Powered by XHack AI for advanced security operations.
6
Organizations trust our cybersecurity expertise
32
Successful security assessments completed
8
Combined team expertise in cybersecurity
24/7
Continuous security operations center
Our mission
Security Operations for Growing Organizations
XHack was founded in December 2025 by cybersecurity practitioners with years of offensive and defensive security experience. We pair that hands-on experience with AI tooling we build and host ourselves.
Today we serve growing businesses with VAPT led by certified testers, red team operations, AI-assisted vulnerability analysis, and 24/7 SOC monitoring. Human analysis does the judging; automation does the heavy lifting.
Whether you need a security assessment, threat intelligence, compliance support, or security automation, XHack can scope it and run it.
Certified cybersecurity professionals with OSCP+, OSCP, and Synack Red Team certifications
Enterprise-grade security solutions and infrastructure
AI-powered security automation for enhanced protection
Trusted by growing businesses and security teams
Team Certifications
Every certification listed is actively held by a team member. No marketing badges: only verified, earned credentials.
OSCP+
Offensive Security Certified Professional PlusOSCP
Offensive Security Certified ProfessionalC-AI/MLPen
Certified AI/ML Penetration TesterVAPT Services · Red Team Operations · SOC & Monitoring · Threat Intelligence · GDPR Compliance · Incident Response
8 Years
Published research
Our Founder's Research, Published by Synack
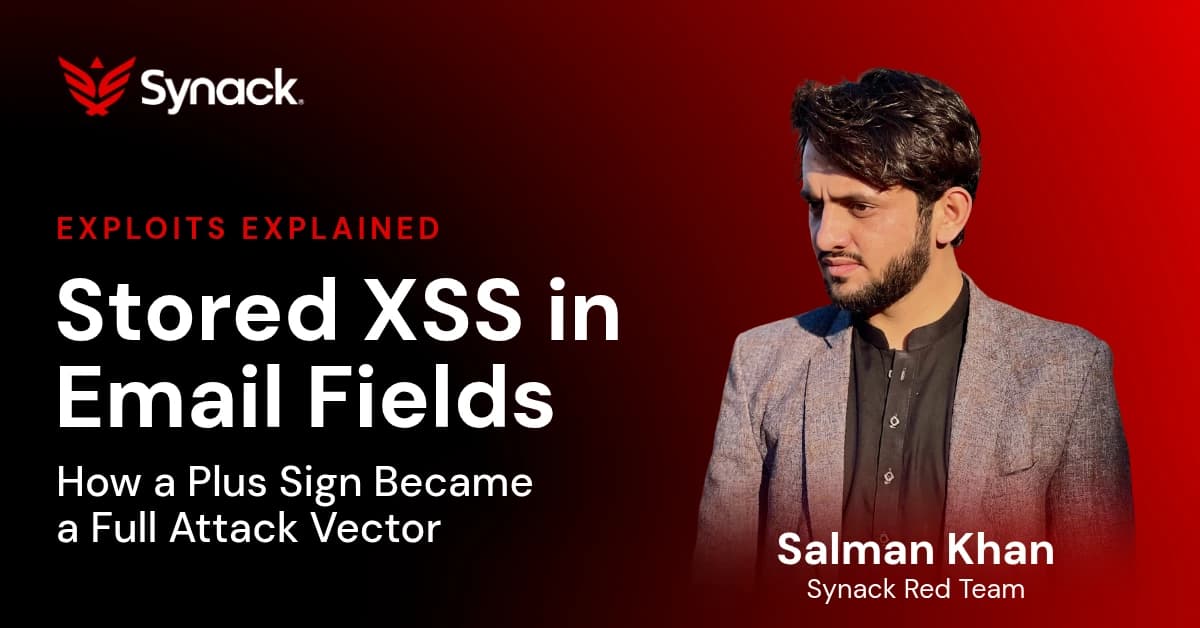
Synack ran Salman Khan's write up in their Exploits Explained series: a harmless looking email subaddress trick turned into stored XSS after bypassing three separate layers of validation on an unauthenticated invite page. The kind of finding that scanners do not report and that only turns up when somebody is actually looking.
Published by Synack as the work of a Synack Red Team researcher. Synack and Exploits Explained are trademarks of Synack, Inc.Where we are
Founded in Pakistan, Working Worldwide
XHack was founded in Pakistan, and our main office is in Peshawar. We are open about that, because the question of where a security team sits deserves a straight answer rather than a vague one. What matters far more is who does the work, what they are certified to do, and what you are contractually owed. Those answers are the same for every client we take on, in every country we work in.
Main office, Peshawar
XHack was founded in Pakistan and our main office is in Peshawar. The whole delivery team sits together, so the researchers who scope your engagement are the ones who run it.
Clients worldwide
We deliver remotely across timezones, in English, on the same engagement model the security industry has used for years. Our clients span SaaS, fintech, e-commerce, EdTech, HR tech, automotive and retail.
Partners wanted
We are actively looking for partners to extend our reach into new regions. If you place security work, resell services, or want a testing team behind your own offering, we want to hear from you.
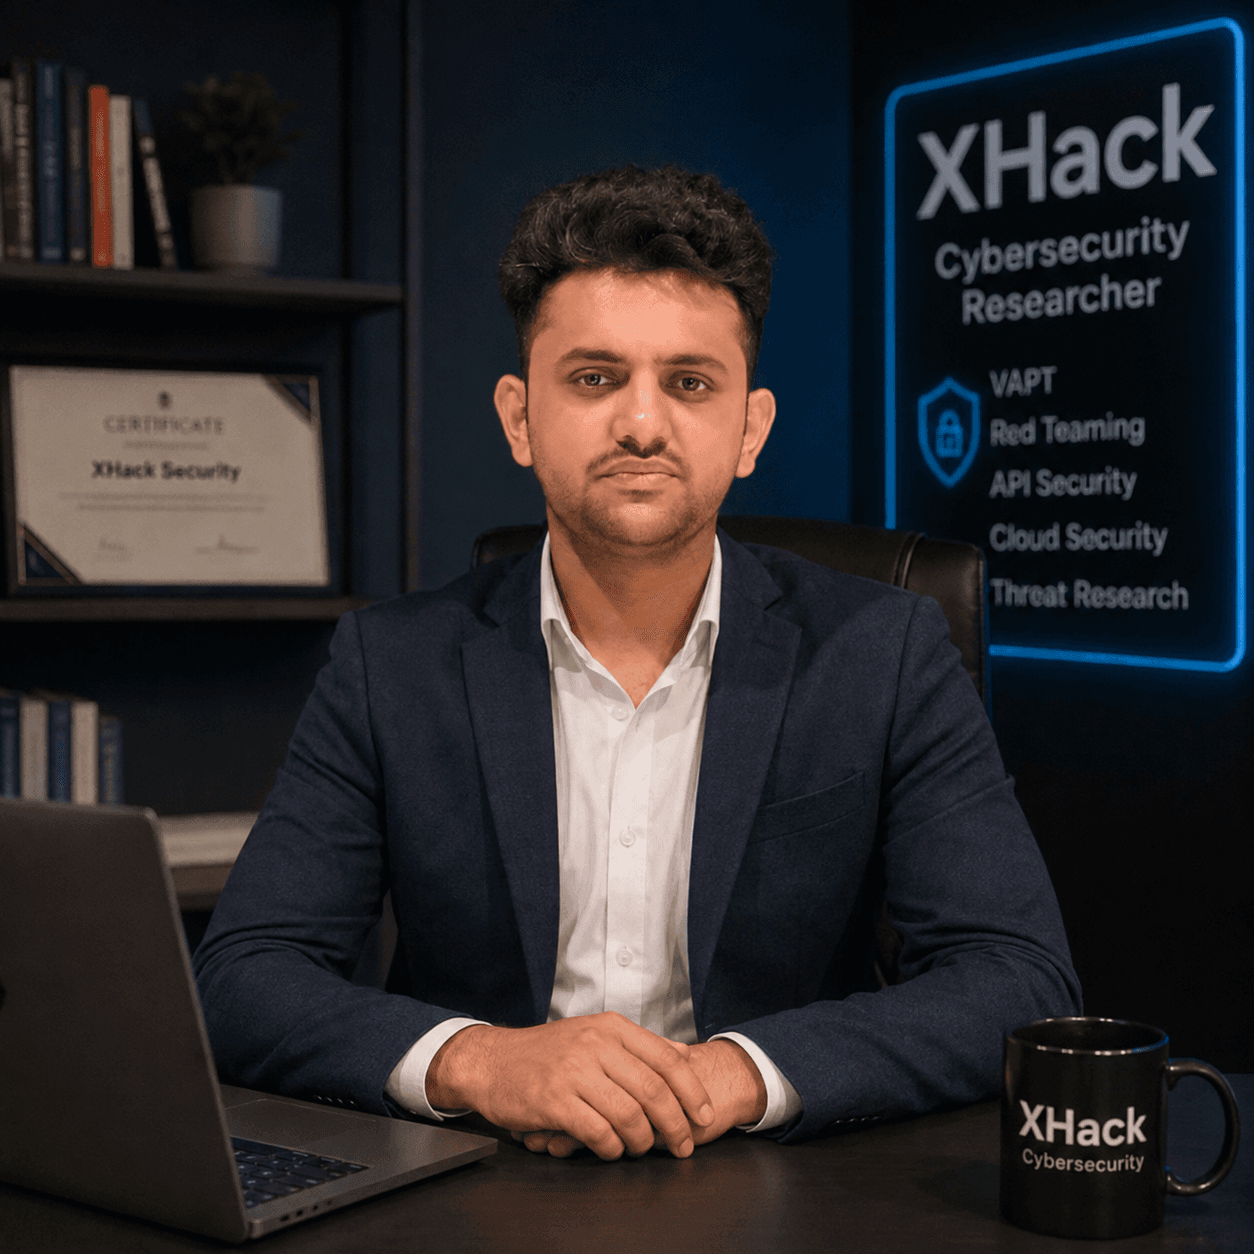
Salman Khan
Founder & Lead Penetration Tester
Peshawar, Pakistan
·8+ Years
Seasoned offensive security professional based in Pakistan with 8+ years of hands-on experience in penetration testing, red teaming, and vulnerability research. An active Synack Red Team member, he leads XHack's mission to deliver enterprise-grade security assessments and has personally led security engagements across web, API, cloud, and mobile targets.
Credentials, each one verifiable
Every engagement is professional. Every product is professional, secure, and in the hands of certified researchers.
That is not a claim about a location. It is a claim about credentials that are verifiable, contracts that are signed before anyone touches your systems, and reports you can hand to an auditor without editing.
What Does Not Change, Wherever You Are
Four things hold for every client, on every engagement, in every region.
Credentials benchmarked globally
OSCP and OSCP+ are the same 24 hour practical exam wherever you sit it, with no multiple choice and no partial credit. Our founder also holds active Synack Red Team standing, a programme that accepts under 10 percent of applicants and whose researchers test Fortune 500 and US federal systems.
Contracts before access
A mutual NDA, a GDPR Article 28 Data Processing Agreement and a written data handling summary are published on this site before you think to ask for them. Nothing starts without written authorisation and agreed Rules of Engagement.
Data handled to one standard
Encrypted in transit and at rest, access limited to the researchers assigned to your engagement, defined retention and secure destruction afterwards. We never share client information, findings or vulnerability detail with any third party.
Reports written for your auditors
Every report is structured for PCI DSS, SOC 2, ISO 27001, HIPAA and GDPR, with methodology, tooling, CVSS scoring, evidence of testing and remediation verification. A sample report is downloadable before you commit.
Our services
Comprehensive Cybersecurity Solutions
Professional security testing delivered by certified engineers, plus the AI tooling to run your security operations day to day.
VAPT & Penetration Testing
Comprehensive vulnerability assessment and penetration testing services to identify and remediate security weaknesses.
Vulnerability Assessment
Penetration Testing
Red Team Operations
Security Audits
AI-Powered Security Platform
Advanced AI tools for vulnerability analysis, security report writing, threat research, and penetration testing assistance.
AI Vulnerability Analysis
Automated Report Writing
Threat Intelligence
Security Research
SOC & Monitoring Services
24/7 Security Operations Center with real-time threat monitoring, incident response, and proactive threat hunting.
24/7 Threat Monitoring
Incident Response
Threat Hunting
Security Analytics
Custom Security Solutions
Bespoke security tools, custom penetration testing frameworks, and tailored security automation solutions.
Custom Security Tools
Automation Frameworks
Security Integrations
API Development
Threat Intelligence
Advanced threat intelligence services including malware analysis, exploit research, and emerging threat monitoring.
Malware Analysis
Exploit Research
Threat Monitoring
Security Advisories
Compliance Testing Evidence
Independent penetration testing evidence for the clauses that require it, in the form your auditor, assessor or regulator accepts.
GDPR Article 32
SOC 2 and ISO 27001
PCI DSS 11.4
Retest Evidence
Our values
What Drives Us Forward
Security First
We prioritize security in everything we do, from our certified professionals to our enterprise-grade solutions. All services are designed for comprehensive cybersecurity protection.
Precision & Accuracy
Our tools and services deliver accurate, actionable results. From vulnerability assessment to penetration testing, expect reliable data you can trust for your security operations.
Customer Success
Your security is our mission. We provide comprehensive support, detailed reporting, and expert guidance to ensure you get maximum protection and value from our services.
Continuous Innovation
We keep building: new AI features, automation tools, and adversarial testing techniques added as threats change. The platform you buy this year is not the platform you get next year.
Ready to Secure Your Organization?
Secure your organization with XHack. Explore our services led by certified testers, AI-powered tools, and comprehensive security solutions today.