
Know what is vulnerable before an attacker does
Vulnerability Assessment is a sophisticated, self-service automated scanner with AI analysis. It sweeps across your verified assets and surfaces black-box vulnerabilities the way an external attacker would find them. You run the scans yourself, watch findings come in live, and the AI handles analysis and reporting so you leave with mitigation plans your team can act on, all inside the XHack platform.
app.xhack.io / va
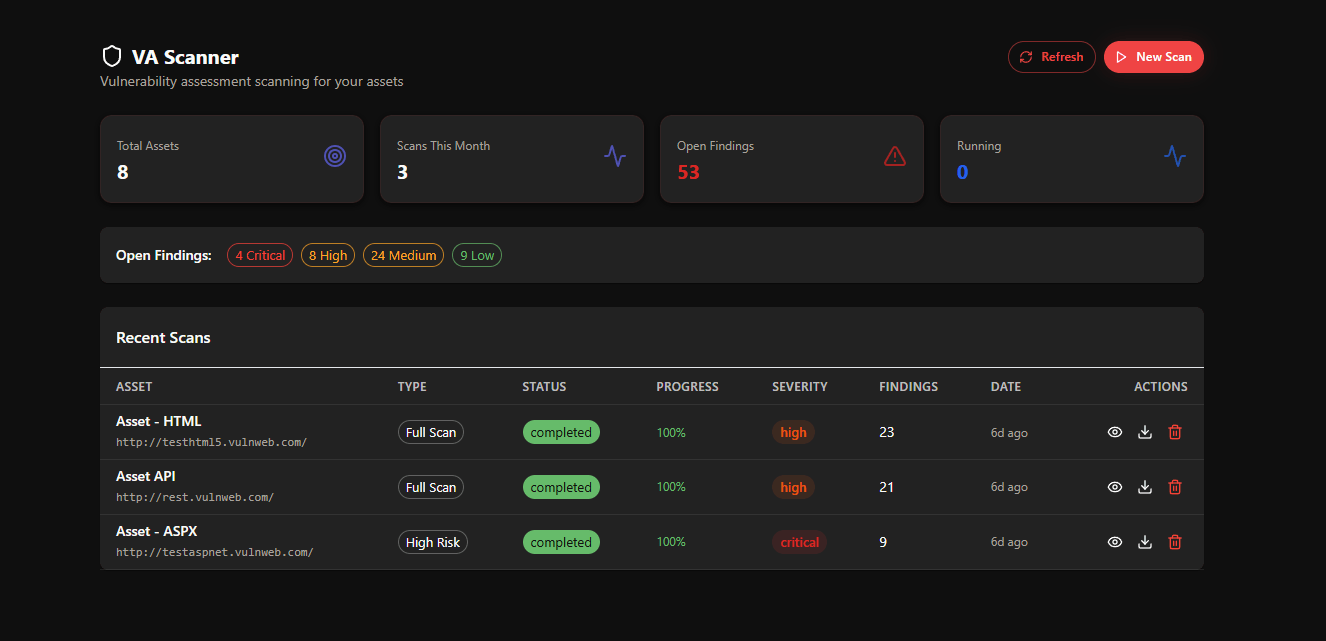
To be clear, this is an automated scanner, not an autonomous agent. Vulnerability Assessment runs the scans you start and hands you analysed findings. It does not plan an engagement, chain attacks or exploit on its own. For a fully autonomous agent that does, see the XHack AI Agent. For testing our team delivers for you, with certified researchers and AI agents working side by side, see managed services.
AI-driven
Scans run and analyse themselves
Live
Findings appear as they are discovered
Dev, CISO & PM
Mitigation plans for each audience
Tenant-isolated
Your assets and results stay yours
What it does
From registered asset to finished mitigation plan
Discover weaknesses across your assets and address them in one place, with AI doing the heavy lifting at every step. Here is the whole product at a glance.
Register and verify assets
Add domains, subdomains, IP ranges, APIs and web apps, then verify ownership so only authorised assets are scanned.
Automated black-box scanning
A sophisticated scanner sweeps across your verified assets and surfaces vulnerabilities from the outside in, the way a real attacker would probe them.
Live progress
Watch vulnerabilities surface in real time as the scan runs, so you can triage early instead of waiting for a report.
Findings detail
Every finding has its own view covering what was found, where, how it can be exploited and the recommended fix.
AI vulnerability write-ups
Generate a deeper write-up for any single vulnerability, with technical context and guidance for the engineer on the fix.
AI mitigation plans
Turn raw findings into structured remediation plans tailored to developers, security leads and project managers.
Shareable reports
Produce full assessment reports with risk ratings, evidence and remediation, ready for teams, clients or auditors.
Plan-based quota
Each plan includes a monthly scan allocation. Delete old scan data and the quota frees up instantly.
Automated scanning is the start, not the finish
Vulnerability Assessment scans and analyses, but it does not exploit or chain attacks on its own. When you need active exploitation, attack-path chaining and real depth, step up to a full penetration test. Deploy the XHack AI Agent to run one autonomously, or have our team deliver it as a managed engagement, where certified researchers and AI agents work side by side.
Start on the right footing
Register and verify your assets
Before running a scan, assets are registered through the platform and go through a straightforward verification step. That way only authorised assets are scanned and every result is tied to the correct infrastructure in your account.
Register domains, subdomains, IP ranges, APIs and web applications.
Verify ownership so scanning is limited to assets you are authorised to test.
Verified assets stay in your inventory, ready to scan again whenever you need.
Results are always attributed to the right asset, with nothing scanned by mistake.
va / assets
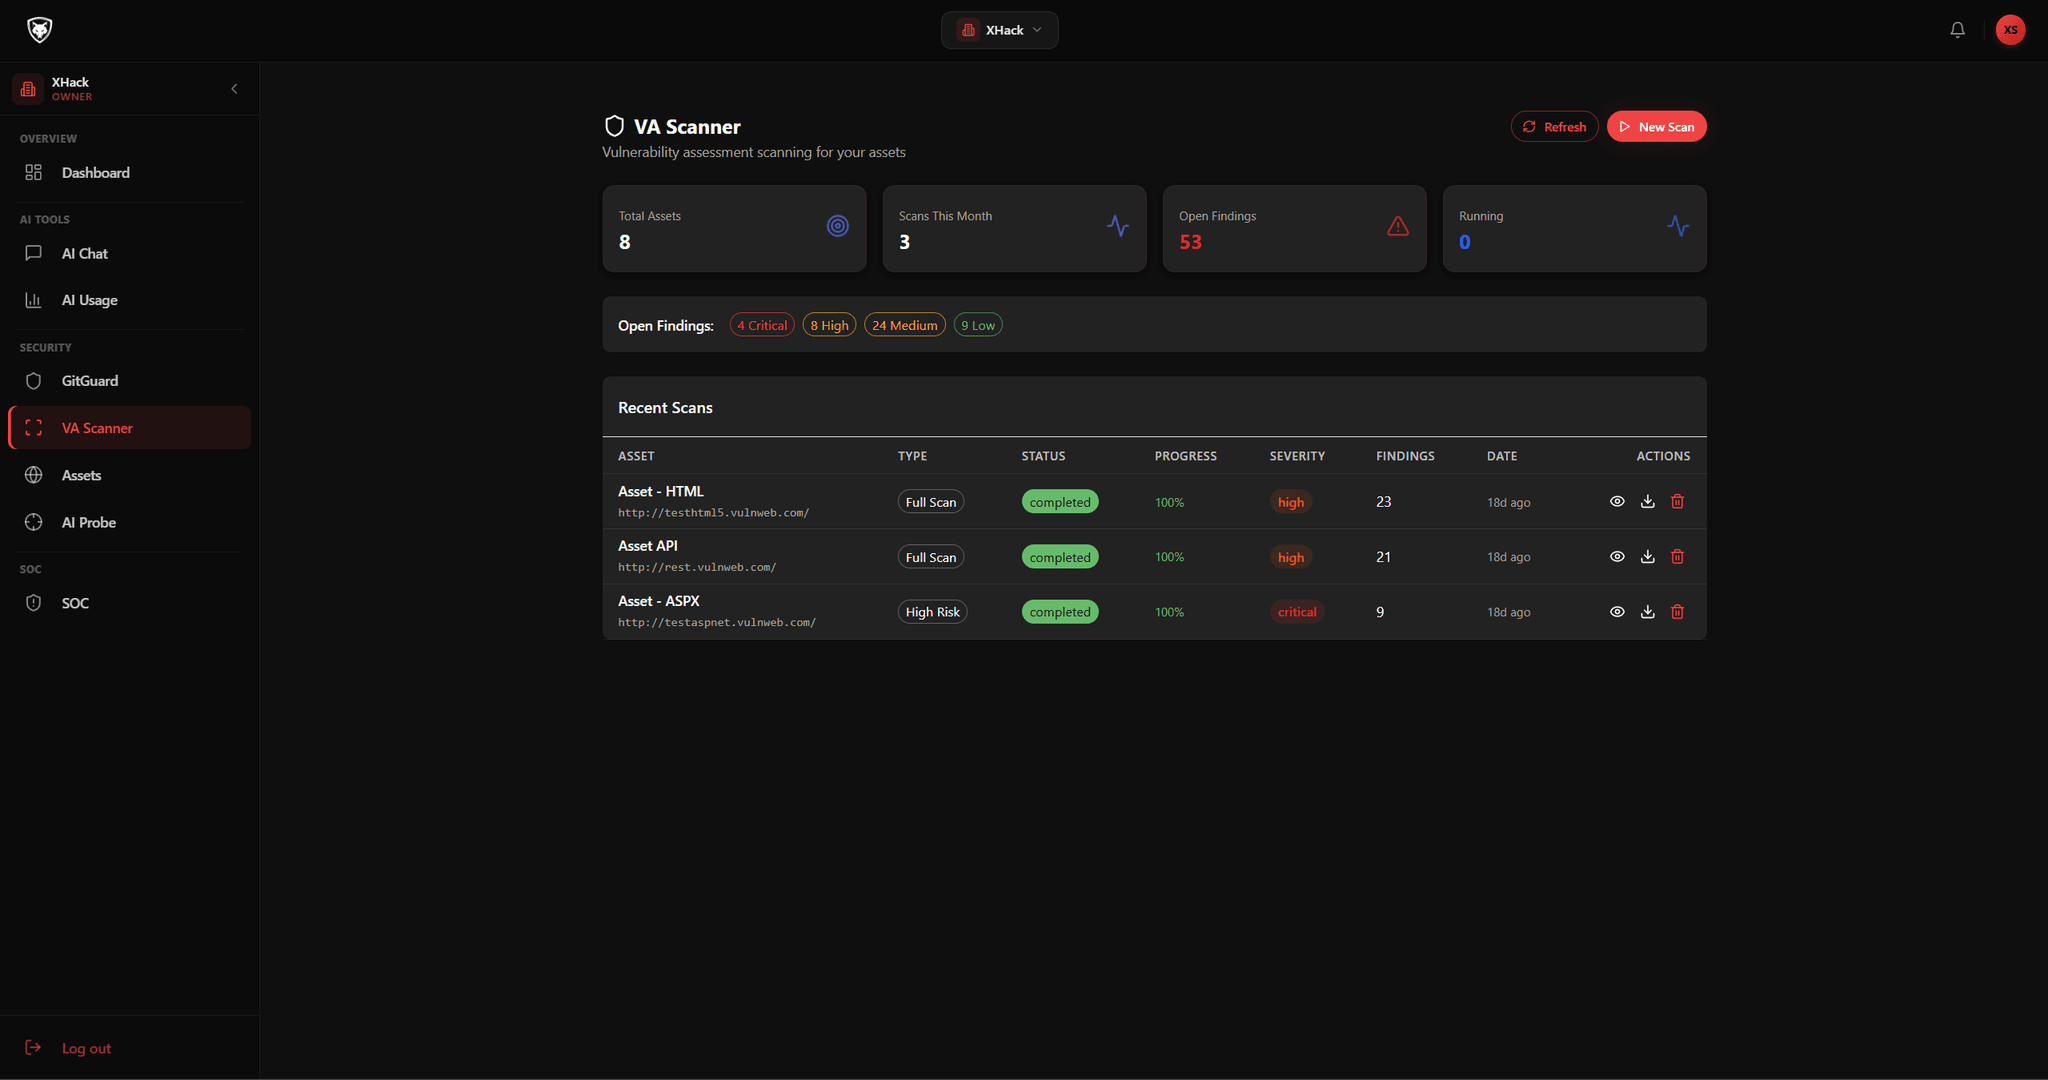
va / live scan
Start it and get on with your day
Watch it live, or walk away
Select a verified asset and kick off the scan. You do not need to stay at your desk for it to be useful, so you choose how you want to follow along.
Stay and watch
Live progress shows vulnerabilities as they are discovered, so you can review findings, triage early and start planning remediation before the scan has even finished.
Or step away
Close the browser and carry on. The scan runs in the background, and we email you when it is complete, or sooner if a high-severity vulnerability needs immediate attention.
Findings that are easy to act on
Every vulnerability, explained in full
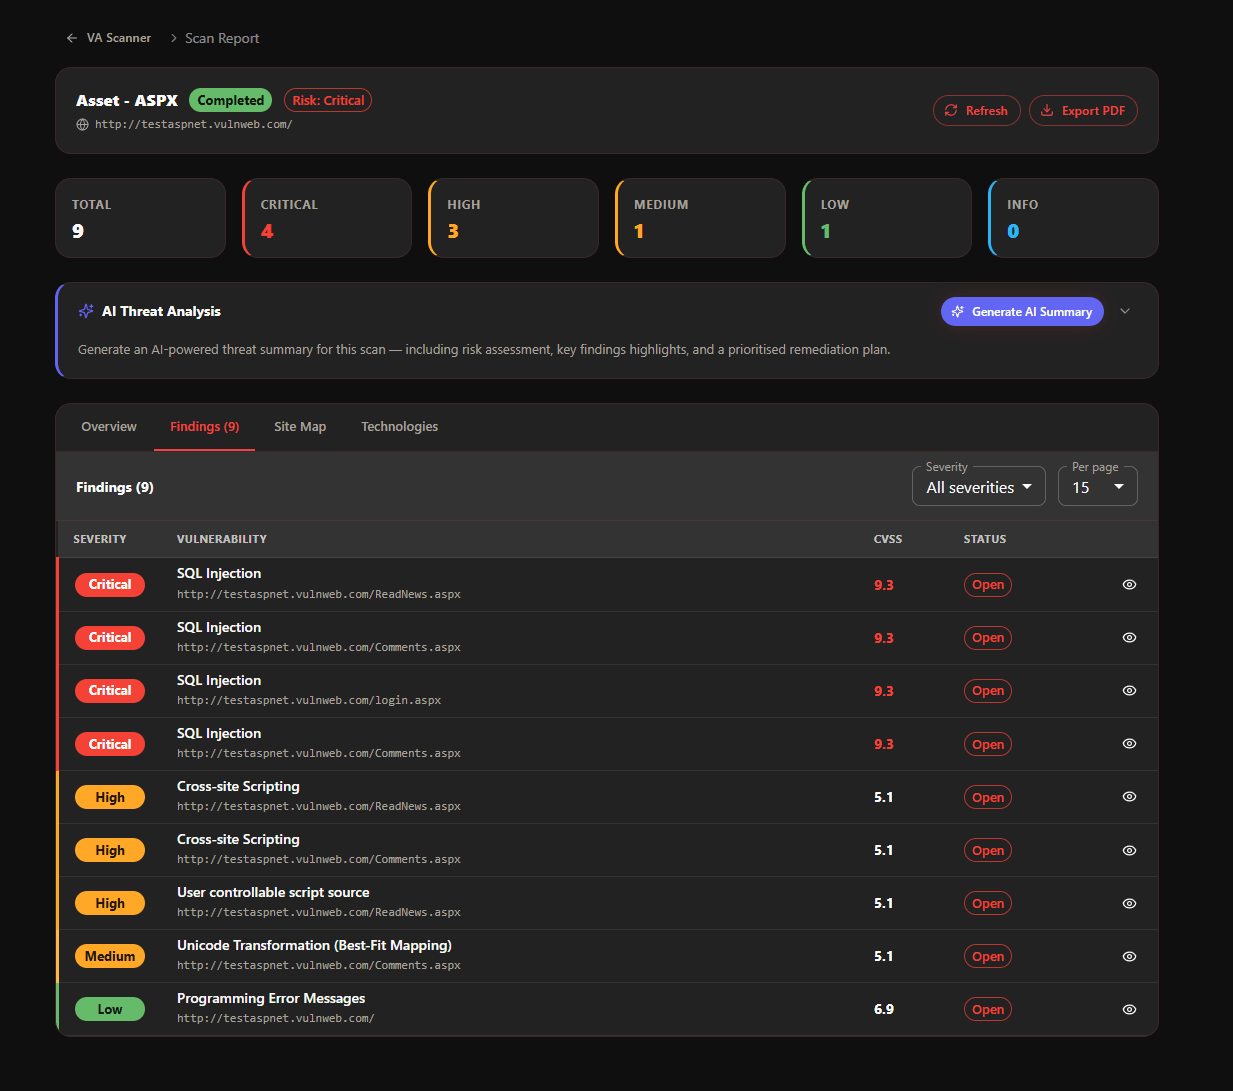
Open any finding for a complete breakdown, and when you need more depth, the AI writes a dedicated analysis for that single vulnerability.
va / vulnerabilities
What and where
Each finding records exactly what was found and the location on your asset, so there is no guessing about scope.
How it can be exploited
A clear explanation of the attack path and the potential impact if the weakness is left in place.
The recommended fix
Every finding arrives with a recommended remediation, so the next step is obvious.
Deeper AI write-ups
For teams that need more, the AI generates technical context, attack scenarios and engineer-specific guidance per vulnerability.
A deeper write-up on demand
For teams that need more than the standard detail, the AI generates a dedicated write-up for any single vulnerability. It covers the technical context, the attack scenarios that matter and specific guidance for the developer or engineer who owns the fix.
AI turns findings into action
One scan, a plan for everyone who needs one
The most useful thing the platform does after a scan is turn raw findings into structured plans that different people can actually use. Each is generated with one click, and can be exported or shared straight from the platform.
For developers
A technical remediation plan
The AI explains exactly what needs to change in the code or configuration, with examples where they help, so the engineer responsible can move straight to the fix.
For a CISO or security lead
An executive summary
An executive-level view of the risk posture, the most critical findings and a prioritised action plan, written for the person who has to make the call on what gets fixed first.
For a PM or team lead
A task breakdown
A breakdown that makes remediation straightforward to assign and track, so the work lands in your planning tools as concrete tasks rather than a wall of findings.
Generated with one click, ready to share
There is no rewriting findings by hand. Pick the plan you need, generate it, and export or share it directly from the platform. The raw findings become a developer task list, an executive briefing and a project plan without anyone retyping them.
va / report
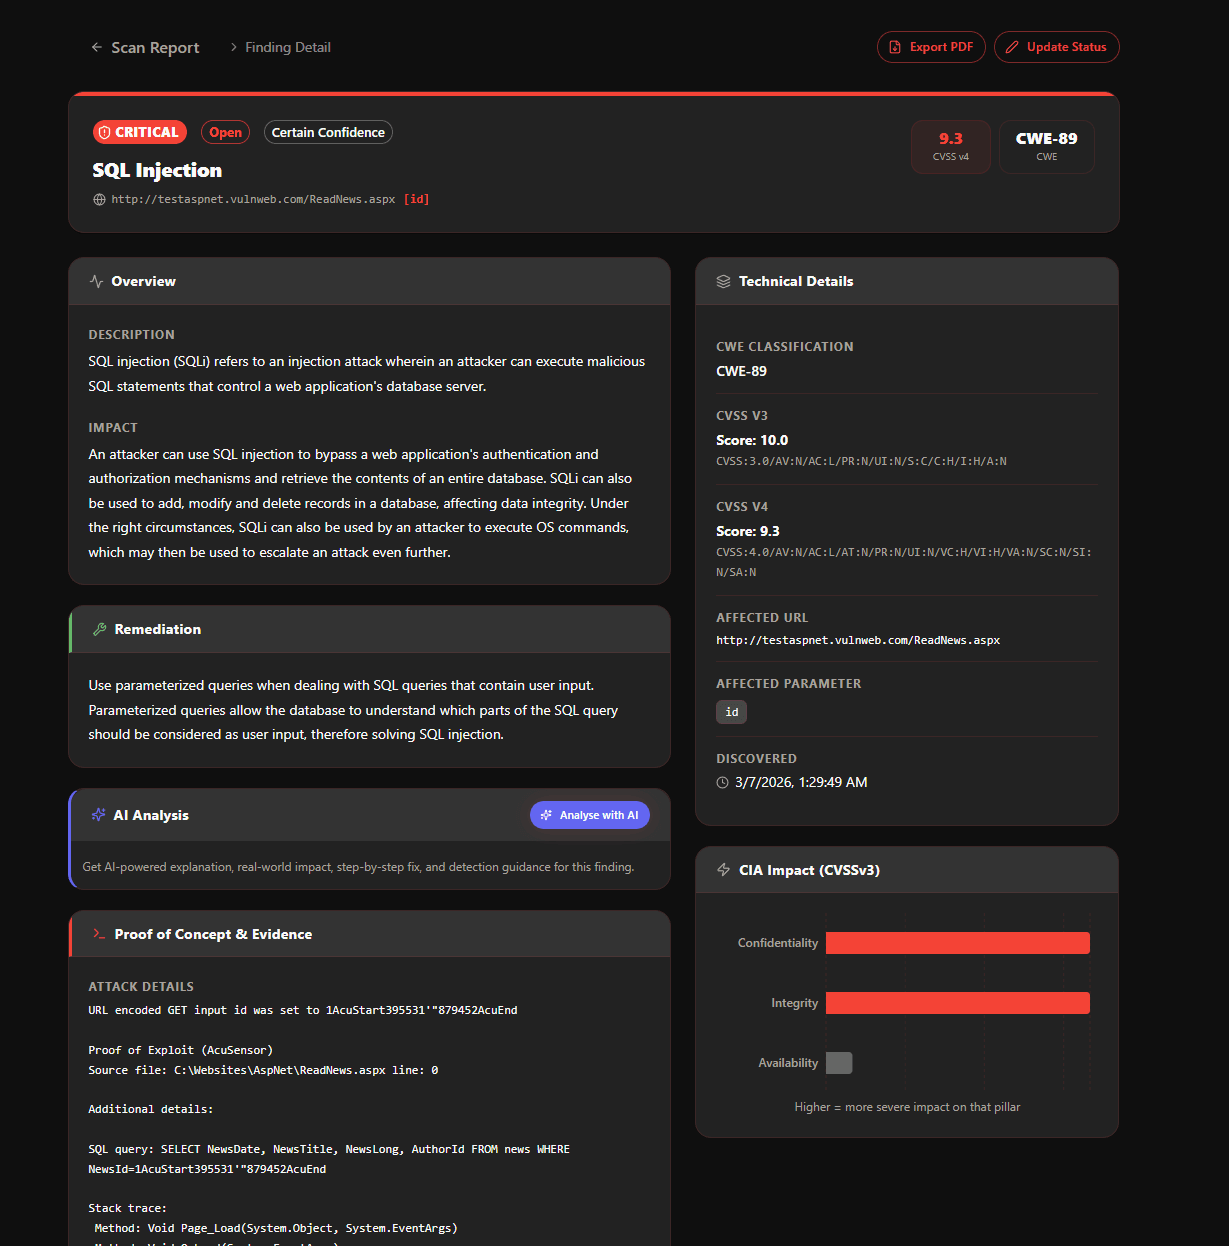
Reports built for real use
A report you can actually send
Generate a full assessment report at any point during or after a scan. It covers the complete set of findings with risk ratings, evidence, technical detail and remediation guidance, formatted so it works as an internal working document and as a formal deliverable for clients, compliance or governance.
Scope by severity
Build a report around critical and high findings alone, or include the full range when you need the complete picture.
Scope by asset
Narrow a report to specific assets or asset groups so each team sees only what is relevant to them.
Scope by time
Report on a specific window, which makes it easy to show progress between one assessment and the next.
Usage and data management
Scan capacity that flexes with your plan
Each XHack plan includes a monthly allocation of VA asset scans, and managing your historical data keeps that capacity working for you.
Monthly VA asset scans by plan
Starter
2 scans per month
Premium
5 scans per month
Elite
12 scans per month
Scan results and findings count toward your plan quota, so you always know where you stand for the current cycle.
Delete frees quota instantly
When you no longer need historical scan data, delete findings and scan records in a couple of clicks.
Deletion is immediate and permanent, so there is no soft-delete limbo to manage.
Deleted records free your quota straight away, giving you room for new scans without waiting for the next billing cycle.
Secure by design
Your assets and results stay yours
The VA platform is built on a multi-tenant architecture, so your assets, scan results and reports are completely isolated from every other organisation on the platform.
No data is ever shared across tenants. What belongs to your organisation stays inside your organisation.
All scan activity is logged, with a full audit trail available from your account.
Access follows the same role-based permissions you use across the rest of the XHack platform.
Isolation and audit, built in
Multi-tenant isolation
Every tenant is walled off from the rest, at the data layer and in every view.
Full audit trail
Scan activity is recorded end to end and available whenever you need to review it.
A closer look
Where the work happens
Your asset inventory, the scan detail view and the per-vulnerability breakdown, all in the same workspace.
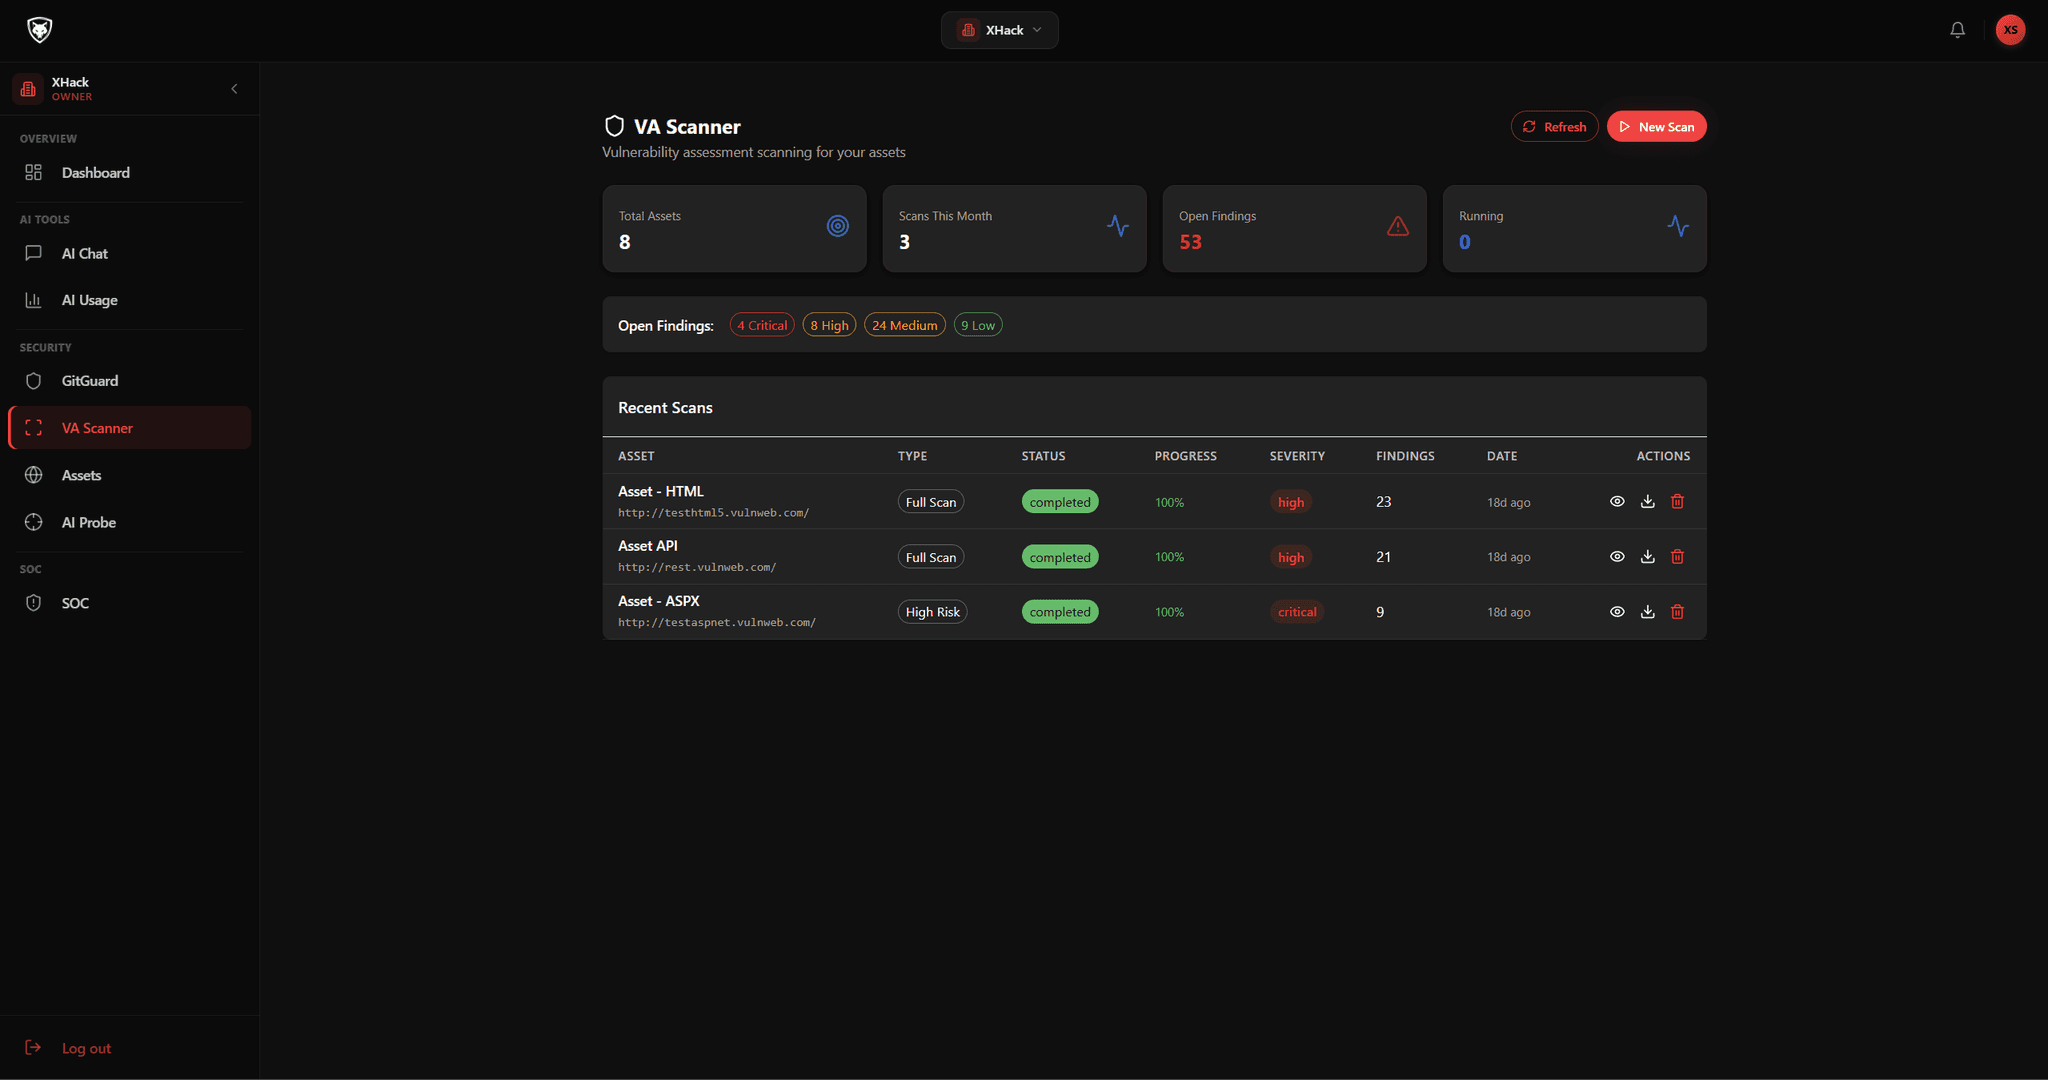
Asset inventory
A single place to register, verify and manage every asset, ready to scan again whenever you need.
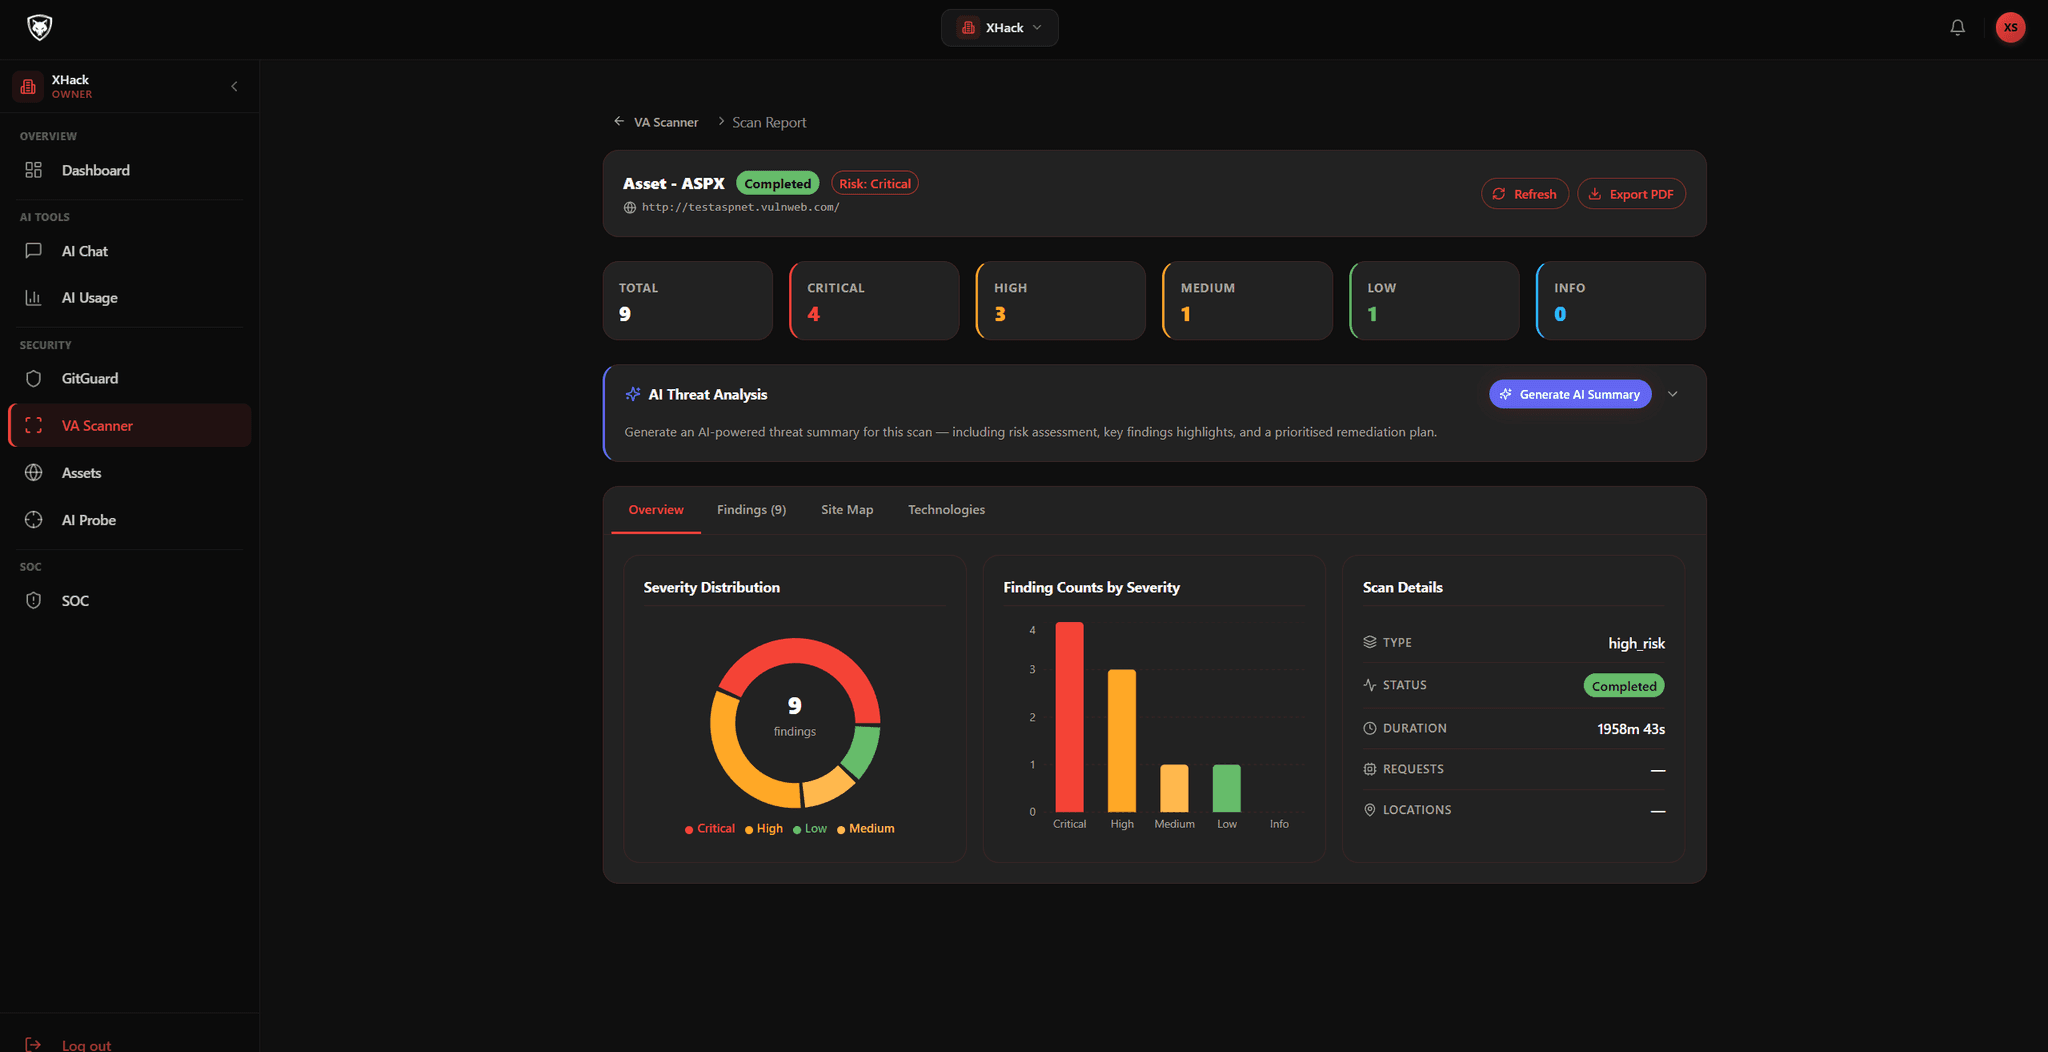
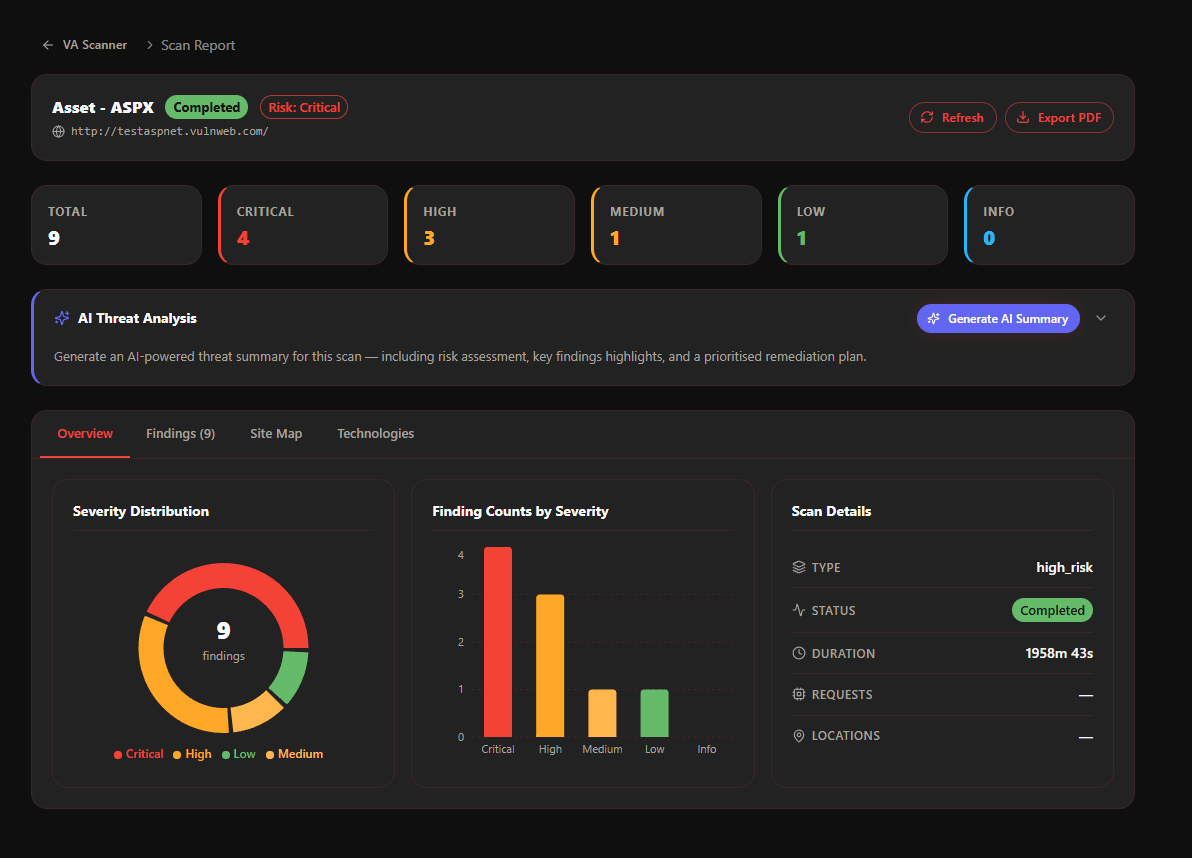
Scan detail
Open any assessment to review its configuration, status and the full set of findings it produced.
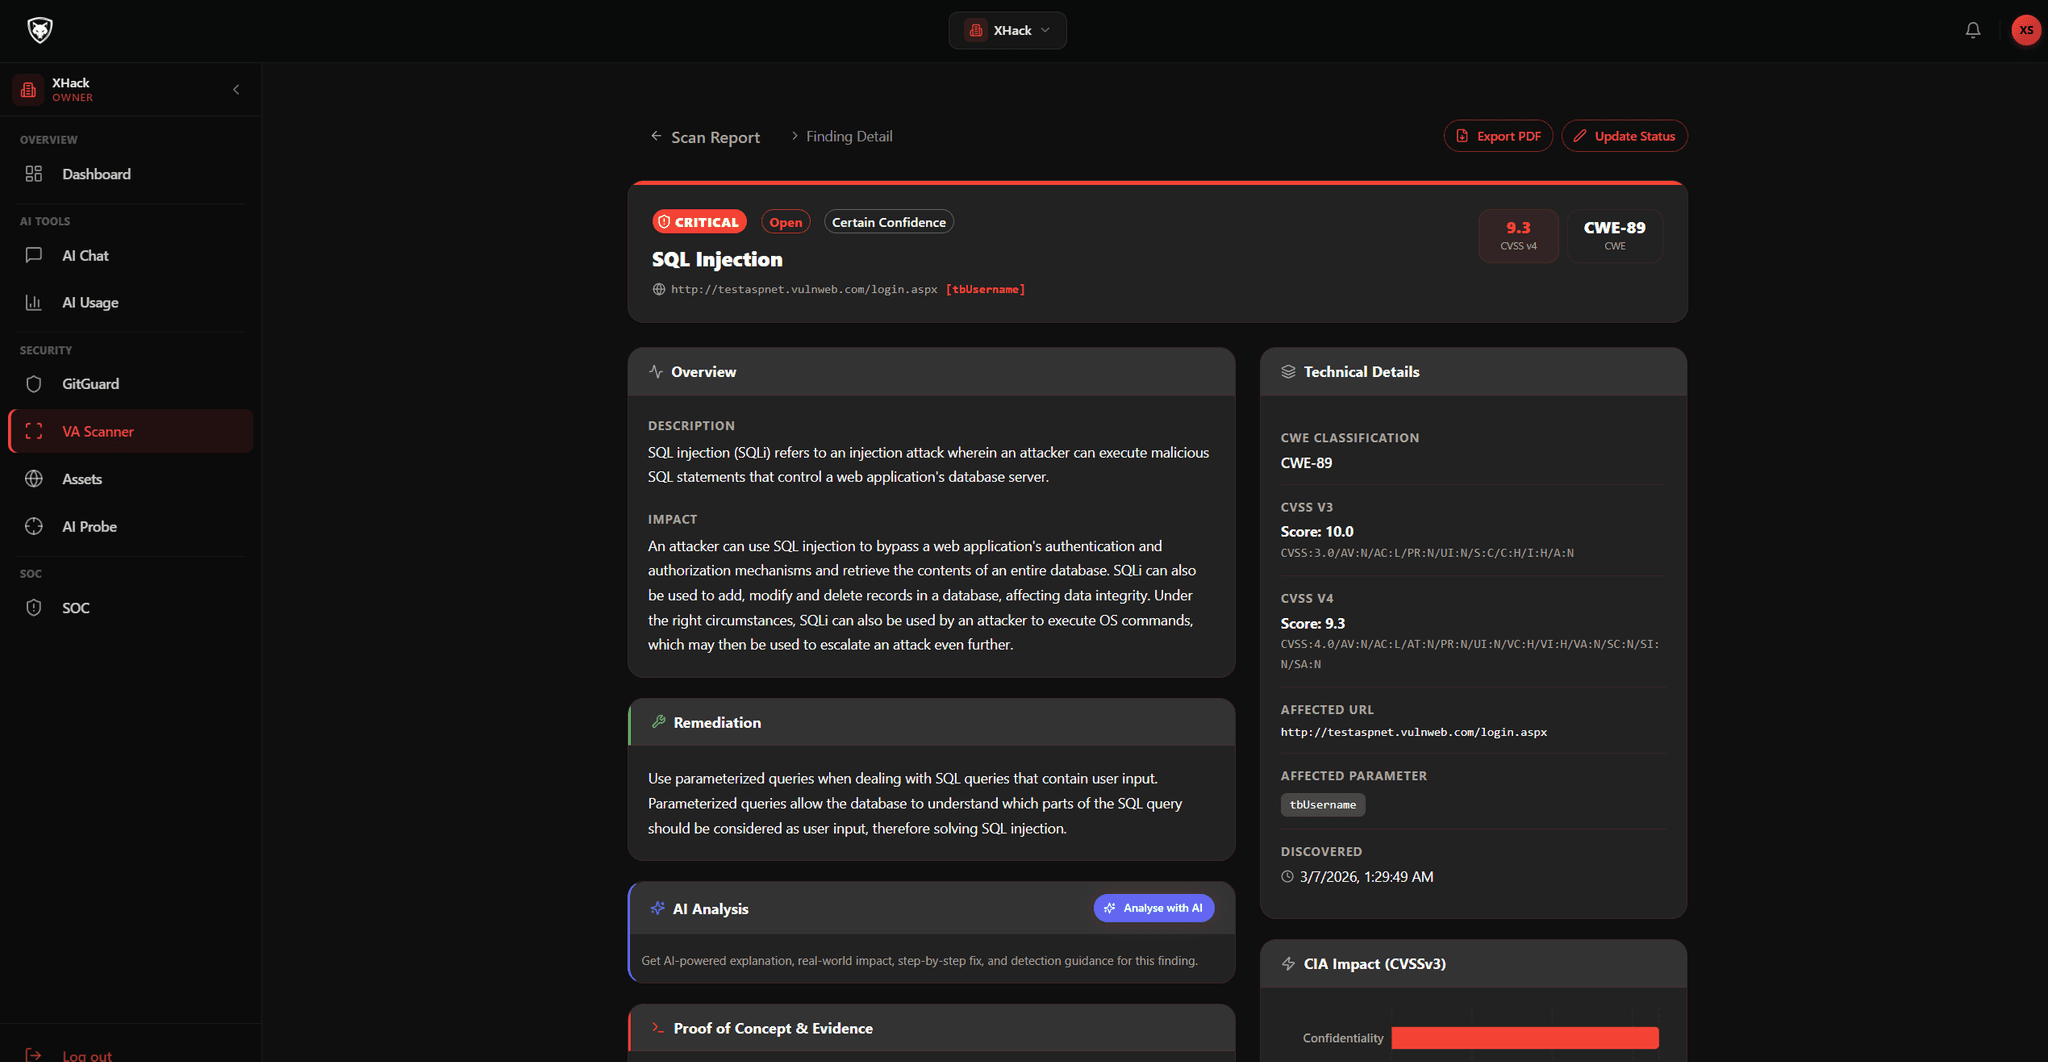
Finding detail
Drill into a single vulnerability for the full breakdown and an on-demand AI write-up.
Questions
Vulnerability Assessment, answered
No. Vulnerability Assessment is a self-service, automated scanner with AI analysis. It sweeps across your verified assets and surfaces black-box vulnerabilities on its own, then the AI writes up the findings and mitigation plans. It is designed for you to run yourself, as often as your plan allows. When you need active exploitation, attack-path chaining and hands-on depth, that is a full penetration test: you can deploy the XHack AI Agent to run one autonomously, or have our team deliver it as a managed engagement, where certified researchers and AI agents work side by side.
Assets can include domains, subdomains, IP ranges, APIs and web applications. Each asset is registered through the platform and goes through a straightforward verification step first, so only authorised assets are scanned and results are always tied to the correct infrastructure in your account.
No. You can stay and watch live progress, with vulnerabilities appearing in real time so you can triage early, or you can close the browser and carry on with your day. The scan runs in the background and we email you when it finishes, and also the moment a high-severity vulnerability is found that may need immediate attention.
In two ways. You can generate a detailed write-up for any individual vulnerability, covering technical context, attack scenarios and guidance for the engineer on the fix. You can also generate structured mitigation plans that turn the raw findings into something a developer, a security lead or a project manager can each act on directly.
Yes. Mitigation plans are generated with one click and can be exported or shared straight from the platform. Full assessment reports cover the complete set of findings with risk ratings, evidence, technical detail and remediation guidance, formatted to work as internal documents or as formal deliverables for clients, compliance and governance.
Each plan includes a monthly allocation of VA asset scans. Starter includes two per month, Premium includes five and Elite includes twelve. Scan results and findings count toward your plan quota. When you no longer need historical scan data you can delete findings and scan records, and deletion is immediate and permanent, freeing your quota instantly so you do not have to wait for the next billing cycle.
The VA platform runs on a multi-tenant architecture, so your assets, scan results and reports are completely isolated from every other organisation on the platform. No data is shared across tenants, and all scan activity is logged with a full audit trail available from your XHack account.
Run your first scan today
Register an asset, start an AI-driven scan, and watch the findings and mitigation plans come together. Start in the dashboard or book a walkthrough with our team.